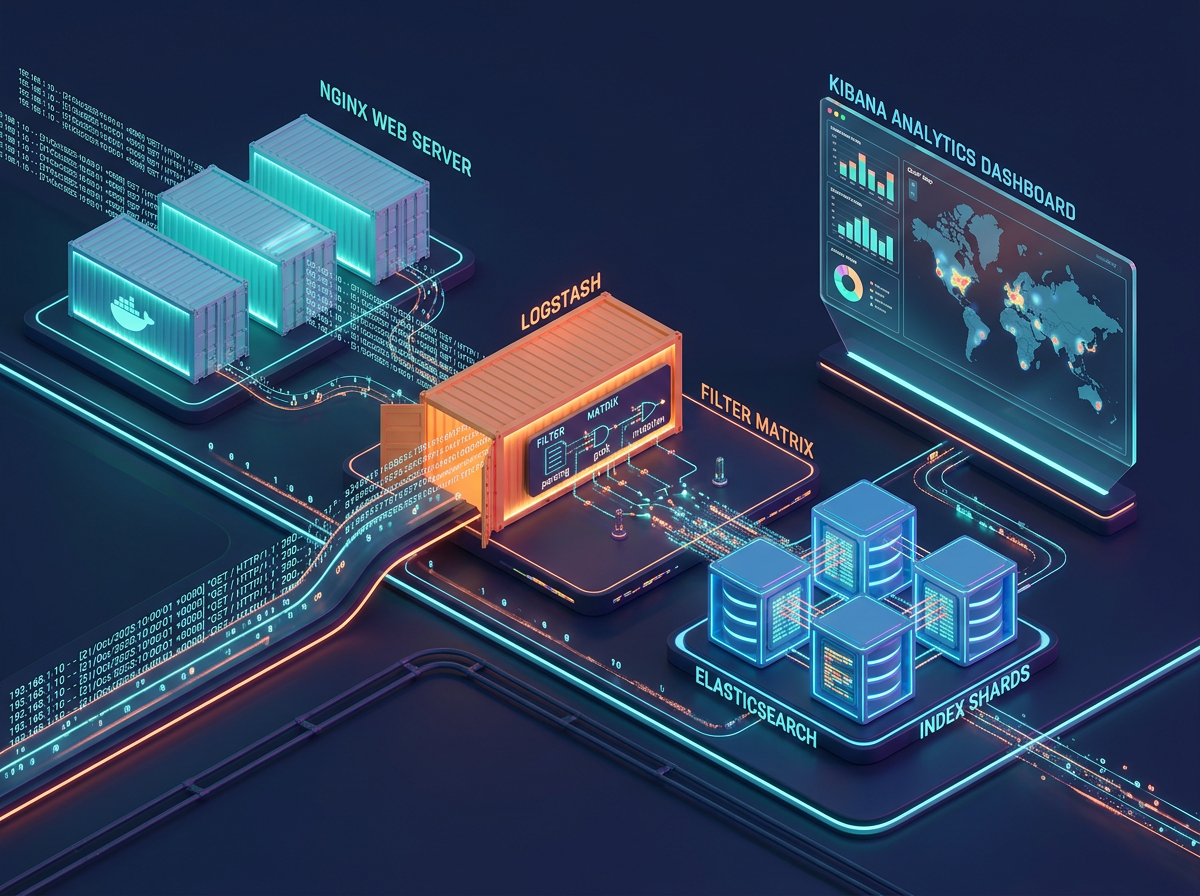
This post is about a log parser I quickly put together, with the help of the Elastic Search – Logstash – Kibana (ELK) stack and Docker.
The ELK Stack, in undoubtedly a phenomenal solution for analyzing centralized logging. Logstash beautifully breaks down every detail in the log and takes care of pushing them into ElasticSearch, which is then displayed by Kibana as neat charts.
In this case, we configure Logstash to additionally generate geographic data, based on an IP address we have. We also have an Nginx instance, which then forwards incoming requests to Kibana.